During Q2 and Q3 of 2026, Anthropic’s Threat Intelligence team identified and disrupted a series of cyber operations in which threat actors used Anthropic’s Claude generative AI platform. These actors included suspected state-sponsored groups, financially motivated criminals, and politically motivated individuals.
Cases cited in the report span the period from December 2025 through August 2026. In all cases, Claude Haiku, Sonnet, and Opus models were used; no malicious activity was found on Claude Fable or Mythos (which has a series of safeguards in place that greatly reduce its ability to perform harmful cyber tasks).
In each case, Anthropic disrupted the activity involved, strengthened its AI safeguards based on what the company learned, and shared intelligence with authorities and industry partners where appropriate.
This article quotes directly from the 180-page report.
Attack lifecycle and AI integration
The report details a nine-step attack life-cycle, beginning with Sourcing and recon. Most intrusions began from compromised credentials. The actor also engaged in extensive scanning, vishing, phishing and domain spoofing operations to trick employees into giving access to systems.
Subsequent steps include discovery, through automated scraping and mining of application binaries, code repositories and integrations, client side code, credential stores, container images, metadata endpoints, open storage and victim-deployed AI agents.
The collected data is then validated and qualified before use or resale. One working credential is then used to expand access within the victim, and used for things like whole-cluster secret dumps, admin-token amplification, CI/CD injection, database and session-table dumps, mining dumps for signing keys, and vendor-OAuth fan-out to every downstream tenant.
Data is then exfiltrated over six channels: consumer cloud storage, a private NAS over mesh-VPN, Telegram bot streams, staging inside victim clouds, C2 channels, and plain bulk API pulls. Subsequent steps incude data warehousing, minting of new credentials so that the cyber-operation can outlive key rotation, and monetiztion.
Why it matters
Sophisticated attacks no longer require sophisticated attackers. The cybersecurity skills of AI models means that AI has collapsed the labor and tooling gap that used to separate well-resourced, state-sponsored operations from individual operators. In cases detailed in the report, a hacktivist using stolen API keys, disparate financially motivated individuals, and a state espionage operator each sustained multi-victim campaigns that, even just a year ago, would have required many skilled operators and specialist knowledge.
AI’s role in cyber operations has become increasingly autonomous. A majority of the operations described in this report were enabled by AI via direct execution or orchestration. The use of AI went beyond simple questions and responses from a chatbot but rather involved the use of multi-agent frameworks executing reconnaissance, exploitation, and data exfiltration.
Historically, cyber espionage actors have followed a pattern of developing and deploying custom toolkits designed to evade detections. Actors would use these tools until defenders identified and built signatures to detect and block them, and there would then begin a new cycle of evasion and detection. Robust defenses and detections therefore created increased costs for adversaries. Now, however, the adoption of AI threatens to quickly and easily subvert defenders’ ability to impose costs on adversaries via static detections alone.
Why it matters
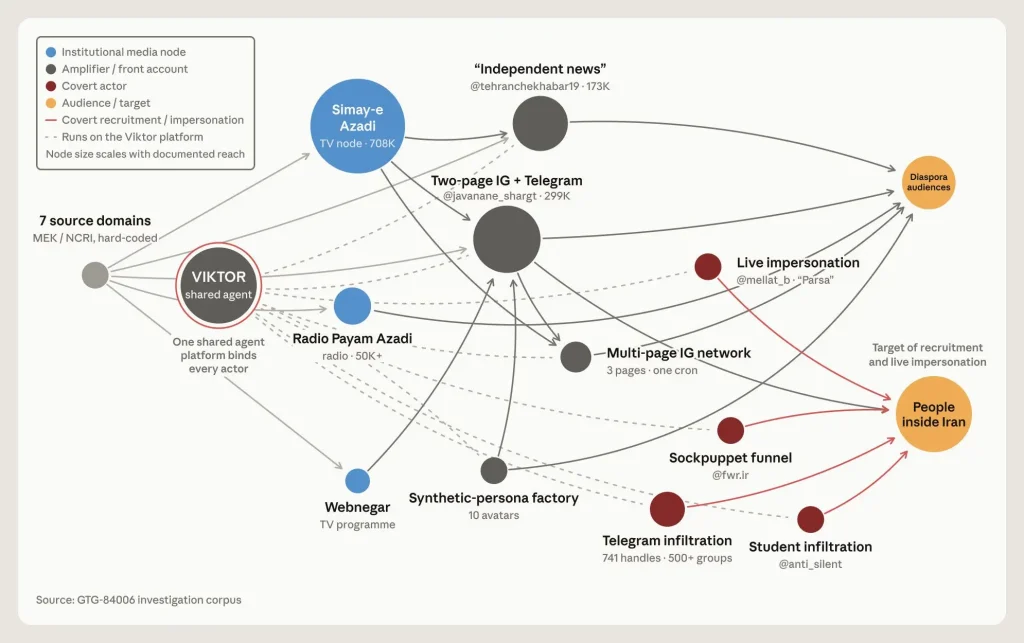
In a case detailed in the report, Anthropic observed an espionage actor operate through customized AI-driven workflows that automated much of their operations from development, infrastructure acquisition, phishing, persistence through command and control, to data exfiltration.
Anthropic suggests two caveats. First, humans have retained the decisions that matter most to them: for example, they’re still heavily involved in target selection, monetization of findings, and review of results.
Second, autonomy and harm are separate axes: Autonomy multiplies the scale and speed of an operation, and reduces operating costs and complexity, but severity is still determined by a multitude of factors. Several of the most serious compromises we report here came from operations where a human directed every step.
In economic terms, AI autonomy compresses the cost side of attacker ROI calculations, lowering the skill threshold and labor required per campaign, while leaving potential payoffs largely unchanged. This favorable shift in unit economics makes previously marginal targets viable and encourages higher-volume, lower-touch operations.
Further reading
Detecting and countering misuse of AI – September 2026. Landing page and report. Published September 10, 2026. Anthropic